Open source · MIT licence · Self-hosted
From application noise to trusted security signal.
Bower collects the security events that matter, removes sensitive details before they are stored, and proves their arrival in Microsoft Sentinel.
tar -xzf bower-collector-offline-0.1.0-linux-amd64.tar.gz
cd bower-collector-offline-0.1.0-linux-amd64
(umask 077; cat >seed/enrolment-token)   # paste the one-time token, then Ctrl-D
sudo ./install.sh --endpoint https://bower-management.example.com/ --environment production
Collectors run on Linux, Windows and containers. The console runs in your tenant.
The management console
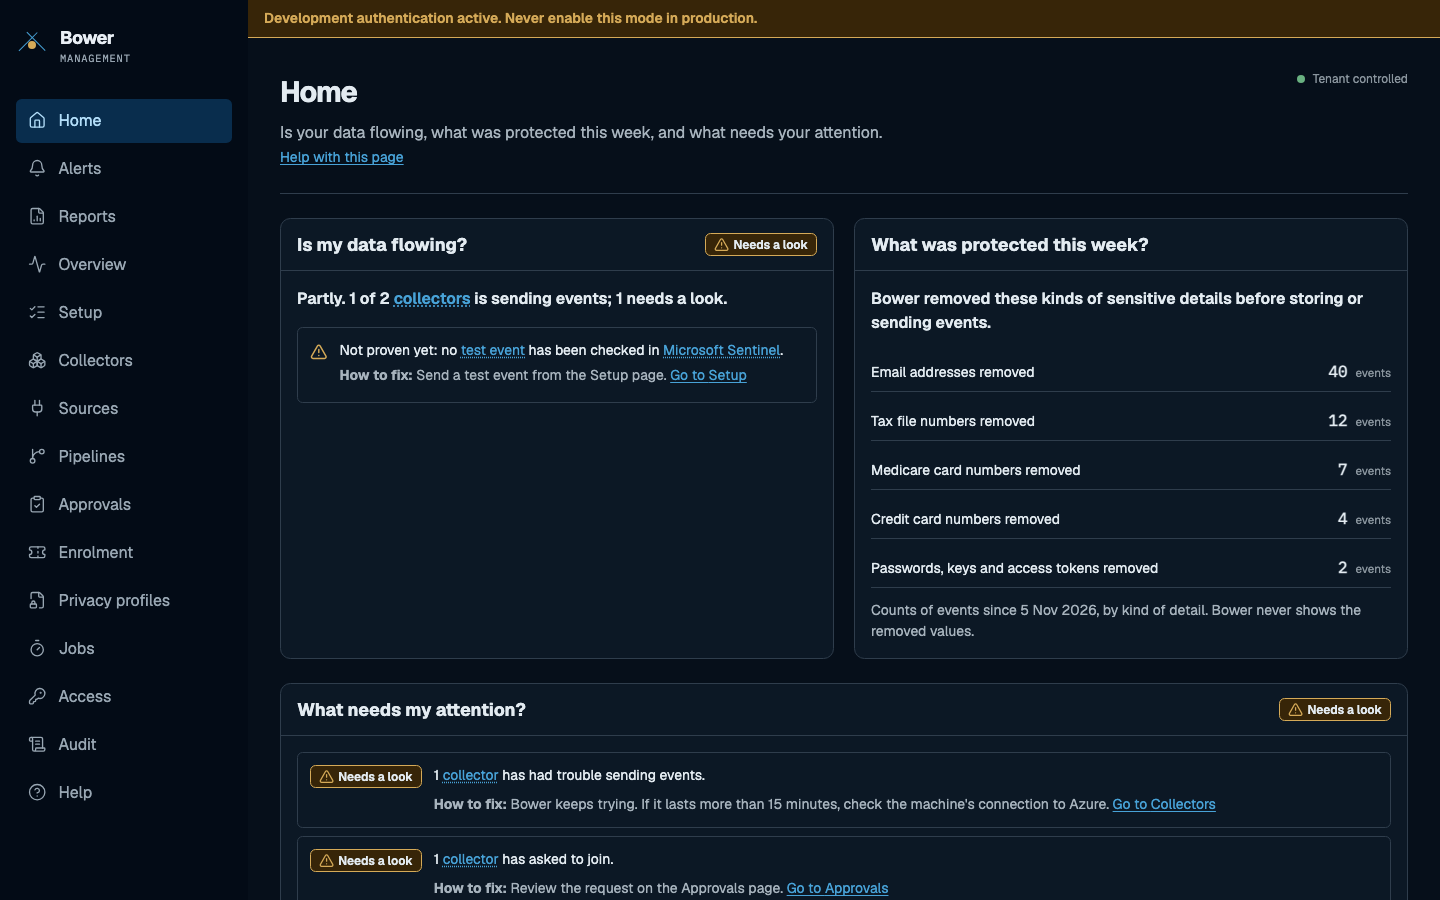
What needs attention, what was protected this week, and collector groups, in plain language.
Read the Home guide →Synthetic preview data. The banner shows the local development sign-in used to capture these; production uses Microsoft Entra ID.
01 How it works
A deliberate path, at every step.
Inspired by the bowerbird, which selects and arranges what is valuable. Bower is a security telemetry bridge, not a general log shipper, a SIEM or a replacement for Azure Monitor Agent.
- 01
Collect
Applications, machines and cloud sources send security events to a collector you run.
- 02
Select
An approved, versioned policy keeps only the event types it names. Everything else is denied and explained.
- 03
Arrange
Events are structured and sensitive details are redacted before anything is stored.
- 04
Deliver
A durable, hash-chained queue delivers with retries, dead letters and audited replay.
- 05
Prove
A canary is queried in Sentinel. An evidence bundle records what was found.
02 What you get
Security events you can trust, and show you can.
Proof of arrival
bower evidence run queries a canary in Sentinel and records the observed result. Acceptance by a collector or an API is never reported as delivery.
Read more →Redaction before it leaves the host
Deterministic, checksum-validated detection of TFN, Medicare, IHI, ABN, ACN, cards and secrets. Any failure quarantines the event.
Read more →Default deny
Only event types an approved policy names are kept. Unknown events are rejected with a reason you can read.
Read more →Delivery accounting
Acknowledged retention, bounded outages, retained dead letters, preflight and DCR drift checks.
Read more →Tamper evidence
A hash-chained queue ledger whose head is witnessed by the management plane.
Read more →Signed packs
Policy, privacy profile, parsers, detections and DCR ship together, signed, hash-pinned and tested before signing.
Read more →03 Deploy
Run it where your events already are.
Start with the guide for your environment, then send your first verified event.
Linux and Windows hosts
deb, rpm and MSI packages, offline bundles and an Ansible role.
Azure Monitor Agent
Send events through local syslog and a collection rule into BowerSecurity_CL.
AWS CloudWatch agent
Write a file the agent ships; the cloud forwarder brings it to the collector.
Containers and sidecars
Collector, console and API images, plus a Docker sidecar for labelled containers.
AWS and Google Cloud
GuardDuty, Security Hub, CloudTrail and Security Command Center through one contract.
Relay networks
Mutual TLS between segmented networks, with an allow-list of collectors.
04 Connect
Sources and frameworks.
SDK guides for common web frameworks, plus host sources selected by signed pack parsers.
- ASP.NET Core
- Next.js
- Express · Fastify · NestJS
- Django · Flask · FastAPI
- Rails
- Laravel
- Spring Boot
- Go log/slog
- Syslog
- Windows Event Log
- Local files
- Docker containers
05 Compare
Bower and a typical log shipper.
From vendor documentation reviewed in October 2026. Local tests do not prove tenant delivery.
| Topic | Bower | Typical alternative |
|---|---|---|
| Proof of arrival | A canary is queried in Sentinel and the result is recorded | Stops at "the API accepted it"; checking Sentinel is manual |
| Redaction | On the host, deterministic, before anything is stored | In Azure after transfer, or a paid redaction processor |
| What is kept | Only event types an approved policy names | Everything configured, filtered later |
| Delivery accounting | Durable queue, dead letters, audited replay, drift checks | Rows can be dropped without a per-record error |
| Tamper evidence | Hash-chained queue ledger, witnessed head | Not offered at the collector |
| Content | Signed, hash-pinned, tested packs | Unsigned community content |
| Where it runs | Your infrastructure; the console belongs to your tenant | Often a hosted control plane |
Send your first verified event.
A harmless test event, through policy, privacy, the queue and delivery, found by a query in Sentinel.